 ← Grupo Aprecisa · Connecting those who know with those who need
State, public works and governance · Article published on LinkedIn on 3 April 2026
The Governance of Critical Infrastructure and Two-Speed Responsibility
Centralising is not protecting: governing critical infrastructure with responsibility at two speeds
Gaspar do Amaral · 3 April 2026
Translated from the Portuguese original. This version was issued on 30 October 2026.
On this site, this article has been
By Eng. Gaspar do Amaral
The planning of infrastructure on a national scale suffers from a chronic illusion: the belief that centralised control equals security. Over decades of integrating land, sea and air transport systems, I have learned that when the State tries to be the “goalkeeper” of a cyber-physical network, it is not building a shield; it is raising a target.
To dismantle this fallacy and design a collapse-proof model, intuition is not enough; the science of complex systems must be called upon. As Donella Meadows details in her magnum opus Thinking in Systems: A Primer, intervening in a system should focus on redesigning its information flows and its penalty rules (the feedback loops), not on micro-controlling its nodes. The State must therefore abandon centralisation and embrace the principle of Two-Speed Responsibility (Responsabilidade a Duas Velocidades).
Pillar I: The Dual Speed and the Transfer of Risk (the End of the State Gateway)
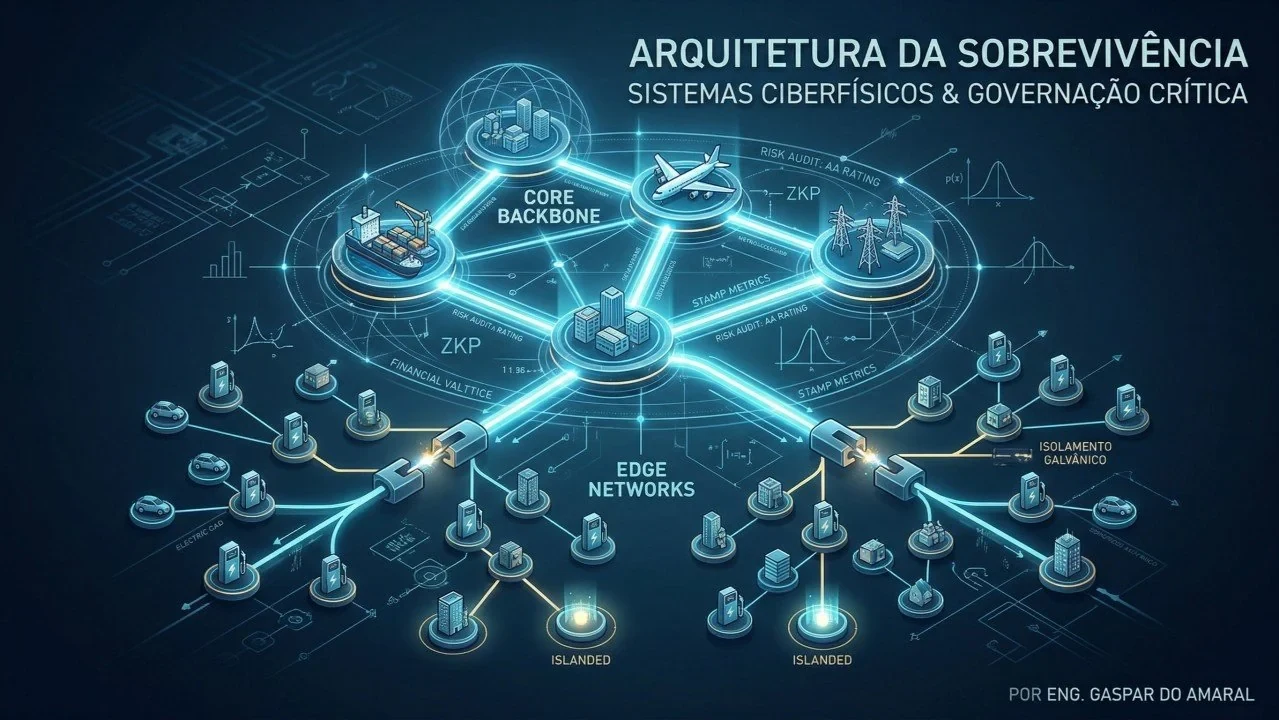
The current architecture treats all infrastructure alike, creating what the sociologist Charles Perrow defines in Normal Accidents as “tight coupling”. If we connect the chargers of retail SMEs to a central State security gateway, an anomaly at the periphery or a direct attack on the centre paralyses the whole country. Engineering requires us to cut this coupling.
For the Core Network (backbone) — airports, ports and intermodal hubs — failure is inadmissible. Yet the audit should not be bureaucratic, but financial. The pioneer Ross Anderson, in Security Engineering, establishes that information security invariably fails when the entity that manages the risk is not the one that pays the bill for the disaster. The solution is to require the audit of the Core Network to be carried out by global reinsurers. We thus apply the central thesis of Nassim Nicholas Taleb in his book Skin in the Game: without the risk of financial and criminal ruin, private operators do not build resilient systems. If the insurance market does not validate the consortium, the State does not issue the licence.
In the Edge Network (urban capillarity), applying this military burden would destroy local SMEs, a scenario against which Prof. Rosário Macário (IST) frequently warns in her studies on transaction costs in transport regulation. For the edge, the requirement moves to the purely electromechanical plane: the mandatory installation of a galvanic isolation circuit breaker. If the software is breached, the station is physically cut off from the national grid, sacrificing the vehicle but saving the nation.
Pillar II: Zero-Knowledge Proofs (Auditing without a Honeypot)
The traditional licensing model requires companies to hand their algorithms over to the State for testing. The expert Bruce Schneier, in his book Click Here to Kill Everybody, warns that these State sandboxes are quickly turned into gigantic honeypots (cyber lures), attracting attacks from hostile States and putting at risk the intellectual property (IP) of global consortia.
Cyber pedagogy offers a solution carved in pure mathematics. Instead of asking for the data, the State demands an equation that attests to the truth. As theorised by Shafi Goldwasser and Silvio Micali in their founding paper “The Knowledge Complexity of Interactive Proof-Systems”, we use zero-knowledge proofs (ZKP). The State dictates the disaster scenario; the operator runs the simulation in its laboratory and returns to the regulator a cryptographic key that irrefutably validates that the system withstood it, without revealing a single line of code. From the standpoint of the information theory taught by Prof. Mário Figueiredo (IST), the State obtains absolute certainty through mathematical entropy, keeping its own system immune to hosting other parties’ data.
Pillar III: Graceful Degradation and Asynchronous Survival (the End of the Induced Blackout)
The most serious weakness of current tender specifications is the requirement for continuous telemetry. If the State requires the station to send a constant heartbeat to authorise operation, an attacker only has to cut a submarine fibre cable — a strategic vulnerability I followed closely when designing systems in South-East Asia — to create an electrical and logistical blackout.
Infrastructure has to learn to operate in the dark. Amory Lovins, in the memorable report Brittle Power commissioned by the Pentagon, proves analytically that grids must have edge autonomy. This is where theory meets the electrical engineering of Prof. João Peças Lopes (INESC TEC), a pioneer of the concept of islanding (island operation). Without communications, the station stops bidirectional integration (V2G) so as not to destabilise the national system, but keeps supplying vital energy from local batteries.
In this scenario of chaos comes the masterly theory of the Portuguese researcher Paulo Veríssimo, set out in his papers on cyber-physical intrusion tolerance. The system abandons the illusion that the firewall is impenetrable; it assumes the enemy is already inside the communications and adopts graceful degradation managed by independent hardware. In addition, security processes stop focusing on component failure and are orchestrated as an integrated control problem, applying the STAMP methodology developed by Prof. Nancy Leveson in her book Engineering a Safer World.
Conclusion
We cannot fight the fluid threats of the twenty-first century with the static regulatory thinking of the twentieth. As Prof. Carlos Fiolhais often argues in his defence of the scientific method applied to the public sphere, political decision cannot override the laws of thermodynamics or the limits of cryptography.
And by aligning our technological infrastructure with the vision of Organisational Architecture championed by Prof. José Tribolet (IST), we realise that the State does not build: the State legislates the mathematics of risk. Two-Speed Responsibility forces the market to be antifragile.
Technical Annex: Summary of Parameters for Public Tender Specifications
To carry this model over into public procurement, the preambles and technical clauses of the tender specifications of the Central Administration (DGEG, AMT, IMT, IP) should mandatorily adopt the following grid:
1. Qualification Criteria for the Core Network (Concessions of Systemic Risk)
- 1.1. Cyber-physical liability insurance: removal of the requirement to hand over detailed software architecture to the State. Replacement by the obligation to present a cyber-risk policy (Cyber Liability Insurance) covering cascading damage to the National Grid, issued by a reinsurer with a minimum “AA” rating.
- 1.2. Intrusion tolerance (STAMP assessment): mandatory demonstration, in the basic design, that the consortium’s telecommunications network has physical segregation (air-gapping) from the automation and injection (V2G) systems.
2. Technical Standards for the Edge Network (Capillarity in Public/Private Domain)
- 2.1. Autonomous galvanic isolation: mandatory integration, in each HPC transformer/charging station (>50 kW), of independent hardware circuit breakers to monitor local frequency (Hz) and physically disconnect from the grid (response time < 20 ms) in the event of software anomalies.
- 2.2. Asynchronous survival (island mode): on total loss of external telemetry for > 30 seconds, the station adopts the “graceful degradation” profile, ensuring minimum charging power from local batteries and immediately ceasing injection into the grid (V2G/V2X).
3. Inspection and Certification Methodology
- 3.1. Auditing through ZKP: every six months the State issues the “Disaster Vector”. The consortium runs it independently and submits the cryptographic ZKP hash on the regulator’s portal within 48 hours. Failure results in suspension of the operating licence.
- 3.2. Delegated inspection: physical audits subcontracted to, and paid for by the operator itself, independent Classification Societies certified by IPQ and CNCS.
Bibliographical References and Structural Contribution to the Proposal
The literature that scientifically validates the structural premises of this Two-Speed Responsibility, by Gaspar do Amaral is detailed below:
International authors
- Nassim Nicholas Taleb — Skin in the Game: his theory proves that centralised systems are fragile. Contribution: basis of Pillar I; forcing financial risk onto the operators ensures that the network decentralises its defences organically.
- Shafi Goldwasser and Silvio Micali — The Knowledge Complexity of Interactive Proof-Systems: Turing Award winners. Contribution: their invention (ZKP) supports Pillar II, allowing a dangerous State sandbox to be replaced by cryptographic auditing.
- Ross Anderson — Security Engineering: pioneer of security economics. Contribution: grounds the use of the reinsurance market as the State’s true auditor, since private capital penalises cyber failure rigorously.
- Charles Perrow — Normal Accidents: sociologist of disasters. Contribution: his thesis on “tight coupling” grounds the refusal to create a central State gateway, supporting galvanic isolation.
- Nancy Leveson — Engineering a Safer World (STAMP): MIT expert. Contribution: teaches that accidents arise from interaction and not from isolated components, supporting the architecture of “graceful degradation” (Pillar III).
- Amory Lovins — Brittle Power: physicist and systems designer. Contribution: shows that centralised electricity grids are indefensible; requires hubs able to operate in “island mode”.
- Bruce Schneier — Click Here to Kill Everybody: cybersecurity expert. Contribution: his thesis that static compliance does not work against dynamic attackers supports the need for ZKP audits based on live attack vectors.
- Jens T. Ditzel / C. Mumenthaler — Swiss Re: Cyber Risk Research: Contribution: actuarial science shows that robust financial models already exist today for the market to absorb the risk of infrastructure networks.
- Richard A. Clarke — Cyber War: American strategist. Contribution: his warning that civilian targets will be the first casualties justifies raising these networks to National Defence Infrastructure.
- Donella Meadows — Thinking in Systems: Contribution: the theory of feedback loops justifies that information delays (internet outages) must not destabilise the physical flow (electricity in island mode).
- Vint Cerf — TCP/IP architecture: father of the Internet. Contribution: the principle of autonomous nodes and decentralised routes is the conceptual model for rejecting State control gateways at the edge.
National authors and researchers (Portugal)
- Paulo Veríssimo — Intrusion Tolerance: Contribution: the paradigm that the system must survive operationally even under enemy control cements Pillar III of our technical proposal.
- José Tribolet — IST / Organisational Engineering: Contribution: validates the thesis that the State must reconfigure its alignment (how it contracts) in order to influence the physical behaviour of consortia.
- João Peças Lopes — INESC TEC / Smart Grids: Contribution: his feasibility simulations of microgrids make the “island mode” requirement an immediate and achievable electrotechnical requirement.
- Nuno Neves — FCUL / Security and Fault Tolerance: Contribution: his research focuses on fault containment, justifying that physical separation (air-gapping) is vital in the face of corrupted software.
- Rosário Macário — IST / Transport Economics: Contribution: her work warns of the inefficiencies generated by heavy regulation, supporting the exemption of the edge from the bureaucratic military burden.
- Mário Figueiredo — IST / Information Theory: Contribution: his application of mathematics to uncertainty validates the use of ZKP as a reliable auditing mechanism without handing over source code.
Methodological note
What this page is. An English translation of the article the author published on LinkedIn on 3 April 2026; the full Portuguese version is on this site. The article contains no calculations of its own; the technical parameters of the annex (>50 kW, < 20 ms, > 30 s, 48 h, “AA” rating) are those of the original.
Changes of form, not substance. In the original, some names carry several links to the same address; here each carries one. The tracking parameters LinkedIn added to some links have been removed. DGEG, AMT, IMT and IP are Portuguese public bodies (energy, transport regulation, mobility and infrastructure); IPQ is the Portuguese Quality Institute and CNCS the National Cybersecurity Centre.
The discussion is on LinkedIn (in Portuguese)
Comments on this text are made on LinkedIn, where the article was shared in Portuguese. You are welcome to write in English. Agree, disagree or add data: every well-founded objection receives a reply.
Gaspar do Amaral · Original in Portuguese of 3 April 2026, published on this site; translation issued on 30 October 2026 · Figures and tables © Aprecisa.com · AI-assisted
How to cite: Gaspar do Amaral (2026). A Governação de Infraestruturas Críticas e a Responsabilidade a Duas Velocidades. Zenodo. https://doi.org/10.5281/zenodo.23814359 · Permanent archive on Zenodo.