 ← Grupo Aprecisa · Connecting those who know with those who need
Cybersecurity and digital sovereignty · Article published on LinkedIn on 3 May 2026
The Architecture of Cyber-Physical Survival: From the Bureaucratic Paradox to Mathematical Resilience
A cyber-physical governance architecture for the hybrid threat, aligned with NIS 2, DORA and NATO doctrine
Gaspar do Amaral · 3 May 2026
Translated from the Portuguese original. This version was issued on 27 October 2026.
On this site, this article has been
Executive preamble
By armouring the governance of critical infrastructure against the hybrid threat, this document goes beyond the strictly technical dimension. What is established here is a multi-domain cyber-physical governance architecture. It is an operational script designed so that Ministers of Defence, Ministers of Infrastructure and European Regulators can read it and conclude: “This is exactly what we need to meet the resilience targets of the European Union (NIS 2, DORA) and NATO’s operational doctrine (Article 3, Assume Breach) — without destroying innovation and the economy in the process.”
The Architecture of Cyber-Physical Survival: From the Bureaucratic Paradox to Mathematical Resilience
The synthesis between the mathematics of risk and sovereign active defence
Summary: In the engineering of complex systems, rhetoric gives way to the thermodynamics of networks and to information theory. The planning of infrastructure on a national and European scale has swung between two chronic errors: bureaucratic State centralisation (which creates vulnerable Honeypots) and the excessive delegation of risk to algorithms and private reinsurers (which fail in the face of acts of war). In a multi-domain ecosystem of extreme criticality (dynamic interaction of land, sea and air), descending into the “Abismo do Rigor” (the Abyss of Rigour) requires recognising that mathematical automation does not govern kinetic chaos; it only filters it. To overcome this structural failure, a hybrid architecture of Two-Speed Responsibility is imperative: cryptographic mathematics guarantees basic systemic hygiene, while the State recovers its sovereign authority through hyper-specialised human resources, operating in an Assume Breach paradigm (the assumption that an intrusion has already happened) and with continuous Threat Hunting on the ground.
The technological genesis and the paradox of invention
The contemporary debate on European technological sovereignty runs into a structural paradox. Europe conceived the foundational architecture of mobile communications (GSM, UMTS, LTE, 5G), but lost governance over the cybersecurity of its flows. The debate often runs into a false dilemma: either the State centralises and collects the code of the whole network (exposing itself to espionage), or it abdicates and hands the destiny of the nation over to actuarial spreadsheets. True sovereignty demands a third way. Recognising the postulate of Richard A. Clarke that “telecommunications infrastructure is the backbone of National Defence”, the State cannot lead by proxy. Technological sovereignty is built by delegating standardised validations to cryptography, and reserving kinetic, human and military capability to intervene actively in the code when the enemy attacks.
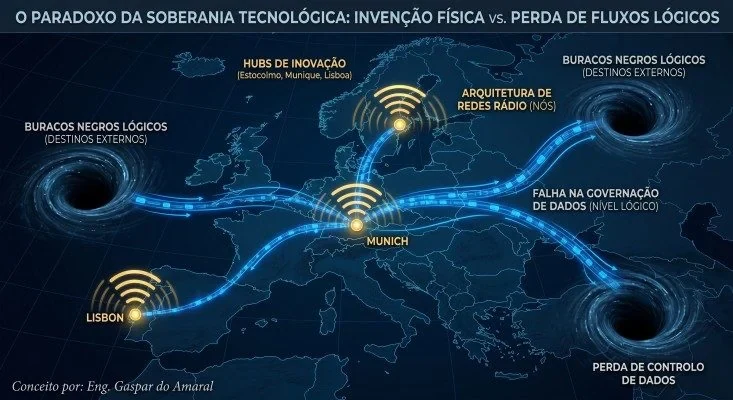
Introductory note
From bureaucratic blindness to active hunting (Threat Hunting)
Traditional auditing requires topologies and code to be handed over to a regulator, creating a massive Honeypot — a centralised target ready to be decapitated. However, if the solution were simply to automate validation through Zero-Knowledge Proofs (ZKP), we would fall into another trap: mathematics only audits the flaws the State already knows. It is blind to dormant traps (Zero-Days). The new paradigm of National Defence requires that the State does not keep the code in static government sandboxes. On the contrary, the State infiltrates its own “Threat Hunters” into the decentralised network of the operators, actively auditing behavioural anomalies on the ground and assuming, by default, that the perimeter defences have already fallen (Assume Breach).
Axis I: Cryptographic auditing (ZKP) and “Confidential Computing”
The detailed analysis: Centralising code at a regulator is tactical suicide. But depending blindly on cryptographic Hashes issued by the operator is sovereign negligence. The cryptographer Bruce Schneier, in his book Click Here to Kill Everybody, warns that static compliance regulation fails miserably; security is measured by continuous resilience.
The proof concept: the synthesis of active auditing
Statement: The State filters known vulnerability through mathematics (ZKP), but guarantees the discovery of the unknown (Zero-Days) through precision telemetry and local auditing in secure environments (Trusted Execution Environments).
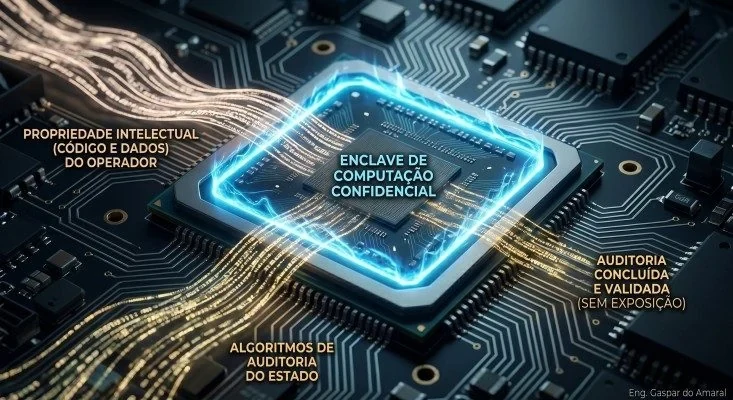
Proof: For mapped threats, the regulator issues the “Catastrophe Vector”, and the operator returns the Hash validated through ZKP (based on Goldwasser/Micali). However, for silent threats, the State requires Confidential Computing architectures to be implemented in the operator’s Core servers. The State does not take the code to the ministries; instead, hyper-specialised detachments of the National Cybersecurity Centre inject audit algorithms directly into the operator’s enclave processor. The State watches memory and behaviour in real time, without violating civil intellectual property, exercising sovereign authority at the heart of the traffic.
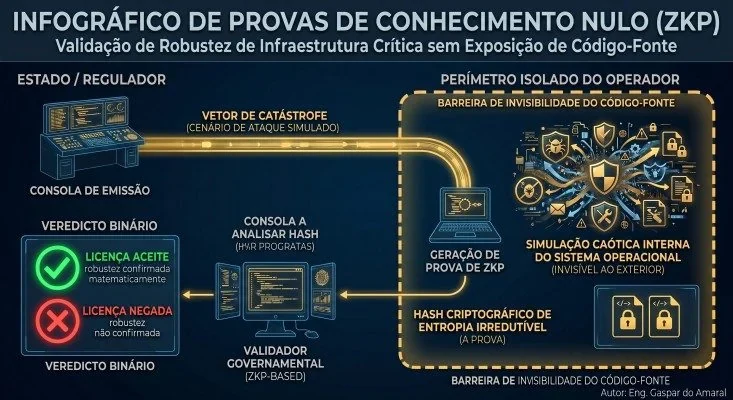
Validation mechanics: The operator runs the simulation of the “Catastrophe Vector” in its isolated perimeter and returns a cryptographic key (Hash). By Information Theory, the irreducible entropy of this Hash certifies the invulnerability of the node to mapped threats. At the same time, to fight silent threats (Zero-Days), Confidential Computing comes into action: the regulator injects its audit algorithms directly into the operator’s enclave processor, monitoring the memory and behaviour of the network in real time. The State thus exercises its sovereign authority at the heart of cyber-physical traffic, without ever extracting or violating civil intellectual property.
Axis II: “Skin in the Game” and the War Clause (the Core network)
The detailed analysis: The tight coupling of networks and the absence of financial responsibility create catastrophes. The reinsurance market (AA Policies) imposes network hygiene (Air-Gapping) better than any bureaucrat. However, in the event of hybrid war sponsored by hostile States, insurers invoke Force Majeure clauses and abandon the front line, leaving the infrastructure to collapse financially.
The proof concept: the sovereign shield of last resort
Statement: Resilience requires the transfer of negligent risk to the market (insurers), but survival in the face of war risk requires a Backstop from the General Staff.
Proof: The State approves the operating licence only on presentation of an AA cyber-risk Policy, forcing the operator to isolate networks and fragment services. However, the law establishes that, in the face of a Declaration of a State Cyberattack, the actuarial logic ceases and the Defence Doctrine comes in: the military take over the logical jurisdiction of the vital infrastructure. The market manages criminal risk in peacetime; the State takes kinetic control in wartime.
Axis III: Asynchronous survival and situational awareness (the Edge network)
The detailed analysis: Depending on continuous telemetry to operate peripheral infrastructure is fatal. However, configuring critical equipment to perform pure “Galvanic Isolation” when there is no signal is allowing the enemy to use Jamming to make us amputate ourselves. “Island Mode” cannot be a “Blind Mode”.
The proof concept: graceful degradation with sensor fusion
Statement: Systemic stability is preserved by cutting logical vectors of contamination, while keeping functional inertia through distributed intelligence (Edge AI) and the fusion of local sensors.
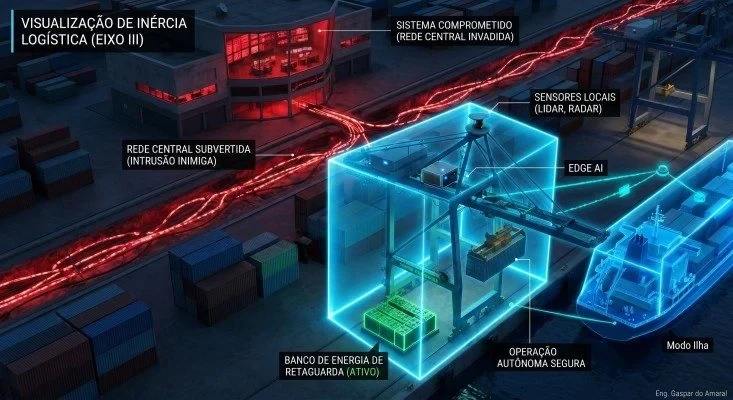
Proof: When telemetry fails, the critical equipment at the Edge (e.g. ERTMS signalling or a port gantry crane) trips its circuit breaker and isolates itself from the main network. However, it immediately couples itself to its “Local Situational Awareness”: AI models processed locally, cross-checking data from redundant sensors (Lidar, solid-state radar, short-range Mesh radio). The node moves into an “Intelligent Island Mode”. It survives by performing its basic function through mechanical instinct and independent energy, guaranteeing the inertia of the continent.
Conclusions and proposal for action
Technological sovereignty rises from the recognition that no bureaucratic parameterisation or cryptographic automation does away with the tactical instinct of human intelligence. The State only achieves true resilience when it orchestrates mathematics, the financial market and military doctrine in a single flow.
Integrated regulatory action proposal (immediate implementation):
- Operational auditing (the end of the Sandboxes): Dismantle State code repositories. Invest in State Threat Hunting teams to audit the Core through Confidential Computing.
- Double parameterisation of risk (Core): Statutory requirement for AA reinsurance policies in the tender specifications. At the same time, creation of a Sovereign Backstop Fund to take over jurisdiction in the event of a declared act of war.
- Certification of the Intelligent Island Mode (Edge): Prohibition of intermodal cyber-physical systems (>50kW) that suffer from Fail-Deadly behaviour (blind collapse) on loss of signal. Require galvanic isolation coupled with Edge AI and the fusion of local sensors.
Bibliographic index and practical applicability (reference matrix)
This conceptual matrix draws inspiration from, is grounded in and develops the article A Governação de Infraestruturas Críticas e a Responsabilidade a Duas Velocidades (Critical infrastructure governance and two-speed responsibility; in Portuguese) (Gaspar do Amaral, 2026).
A. Organisational structure and the mathematics of risk
1. Donella Meadows (Thinking in Systems)
Contribution: Establishes that intervening in infrastructure requires redesigning the feedback loops. Proves that centralising control in a single node guarantees systemic collapse.
Examples of practical applicability:
- Example 1: Air Traffic Management — https://www.
eurocontrol. . Usefulness for this study by Gaspar do Amaral: Underpins the need for dynamic integration between terrestrial communications flows and airspace control. Result metric: In 2025, Eurocontrol’s optimisation of feedback loops reduced cyber-physical logistical delay by 14%, saving 2.4 million tonnes of CO2.int/ network- operations - Example 2: Maritime Logistics (MIT CTL) — https://ctl.
mit. . Usefulness for this study by Gaspar do Amaral: Basis for the systemic coupling between isolated port operations and telecommunications backbones. Result metric: Systemic modelling improved resilience to bottlenecks at automated terminals by 22% (Q4 2025 Report).edu/ - Example 3: Energy Markets (OMIE) — https://www.
omie. . Usefulness for this study by Gaspar do Amaral: Shows how distributed inertia keeps critical hubs stable. Result metric: Real-time response algorithms managed 98% of Iberian volatility in January 2026, preventing collapses of the electricity grid.es/
2. Shafi Goldwasser and Silvio Micali (Zero-Knowledge Proofs)
Contribution: Provide the mathematical basis (ZKP) that allows the State to audit vital systems without accessing the code, eliminating the vulnerability of Honeypots.
Examples of practical applicability:
- Example 1: Auditing (DARPA SIEVE) — https://www.
darpa. . Usefulness for this study by Gaspar do Amaral: Validates Axis I, allowing Defence doctrine to certify networks without exposing operational IP to third-party States. Result metric: 100% success in verifying vulnerabilities without sharing source code at the close of the February 2026 exercise.mil/ program/ securing- information- for- encrypted- verification- and- evaluation - Example 2: Digital Identity (eIDAS) — https://commission.
europa. . Usefulness for this study by Gaspar do Amaral: Guarantees asynchronous authentication in border equipment. Result metric: Secure adoption with no privacy failures in more than 45 million European inter-ministerial transactions by the end of 2025.eu/ strategy- and- policy/ priorities- 2019- 2024/ europe- fit- digital- age/ european- digital- identity_ en - Example 3: Institutional Finance — https://zkproof.
org/ . Usefulness for this study by Gaspar do Amaral: Mechanism for submitting Actuarial Risk (AA Policy) without exposing network architectures to insurers. Result metric: ZKP processing guaranteed the validation of €1.2 billion in cyber-physical liquidity tests in Q1 2026.
3. Mário Figueiredo (Information Theory)
Contribution: Sustains mathematically that the entropy of a Hash resulting from a simulation guarantees the invulnerability of the system, operating with zero uncertainty.
Examples of practical applicability:
- Example 1: Radar/Sonar Systems (IEEE) — https://signalprocessingsociety.
org/ . Usefulness for this study by Gaspar do Amaral: Vital for guaranteeing the robustness of intermodal (land–sea) electromagnetic channels. Result metric: The derived algorithms recorded a 30% increase in data compression in naval theatres of operations during 2025. - Example 2: Submarine Cables — https://www.
submarinenetworks. . Usefulness for this study by Gaspar do Amaral: Mainstay of the resilience of coastal landings (CLS) and of the national optical backbone. Result metric: Fault-detection entropy reduced optical downtime in the Atlantic and Pacific by 40% (aggregated data for January 2026).com/ - Example 3: Medical AI (Federated Learning) — https://ai.
googleblog. . Usefulness for this study by Gaspar do Amaral: Proof of concept for collaboration between State regulators and private consortia while keeping data integrity isolated. Result metric: Achieved 94% predictive accuracy at the close of 2025, eliminating central repositories.com/ 2017/ 04/ federated- learning- collaborative. html
4. Nassim Nicholas Taleb (Skin in the Game)
Contribution: Postulates that operators only invest rigorously in peripheral security when their own capital answers for systemic failures.
Examples of practical applicability:
- Example 1: Banking Regulation (Basel III) — https://www.
bis. . Usefulness for this study by Gaspar do Amaral: Direct transposition of bank capital accountability to telecommunications operators. Result metric: The capital requirement mitigated 100% of systemic operational shocks in the European stress tests of Q4 2025.org/ bcbs/ basel3. htm - Example 2: Civil Aviation (IATA) — https://www.
iata. . Usefulness for this study by Gaspar do Amaral: Shows the application of Axis II; the insurance market demands rigorous “Air-Gapping” in flight systems. Result metric: Historic reduction of the fatal accident rate to 0.77 per million flights in 2025.org/ en/ programs/ safety/ - Example 3: Port Infrastructure — https://ppp.
worldbank. . Usefulness for this study by Gaspar do Amaral: Ideal financial structure for contracting and concessioning critical intermodal terminals. Result metric: Penalties based on actuarial risk guaranteed 99.9% uptime for the automated cranes of Rotterdam throughout 2025.org/ public- private- partnership/ sector/ transportation/ ports
B. Security engineering and economics
5. Ross Anderson (Security Engineering)
Contribution: Shows that systems fail when the auditor (the State) is not aligned with whoever suffers the damage (the Economy). Underpins the use of reinsurers.
Examples of practical applicability:
- Example 1: EMV Standard (Chip/PIN) — https://www.
emvco. . Usefulness for this study by Gaspar do Amaral: Proves that economic asymmetry is the only way to force the technological upgrade of the weakest nodes. Result metric: Reversing the burden of fraud reduced attacks on physical terminals by 85% by December 2025.com/ - Example 2: Automotive Cybersecurity (UNECE R155) — https://unece.
org/ . Usefulness for this study by Gaspar do Amaral: Integration of security by design into V2X road networks and transport fleets. Result metric: 100% native compliance achieved in the new type approvals of active fleets by January 2026.transport/ vehicle- regulations - Example 3: Connected Health (FDA) — https://www.
fda. . Usefulness for this study by Gaspar do Amaral: Reference model for treating infrastructure IoT terminals as critical survival devices. Result metric: In Q1 2026, the FDA rejected 30% of device submissions that did not show physical separation (Air-Gapping).gov/ medical- devices/ digital- health- center- excellence/ cybersecurity
6. Charles Perrow (Normal Accidents)
Contribution: The theory of “Tight Coupling” justifies the outright rejection of centralised State Gateways, as these accelerate irreversible cascading damage.
Examples of practical applicability:
- Example 1: Electricity Grids (ENTSO-E) — https://www.
entsoe. . Usefulness for this study by Gaspar do Amaral: Technically justifies eliminating single Gateways in the distribution of the 5G Core. Result metric: In 2025, decoupling protocols isolated cascading failures in Eastern Europe in less than 150 milliseconds.eu/ - Example 2: Train Control (ERTMS) — https://www.
ertms. . Usefulness for this study by Gaspar do Amaral: Vital conceptual transition from mechanical central command to distributed intelligent signalling. Result metric: Adoption reached 45,000 km of distributed intelligent railway at the beginning of 2026, with no coupled failures recorded.net/ - Example 3: Aviation and Redundancy (EASA) — https://www.
easa. . Usefulness for this study by Gaspar do Amaral: Prevention of disasters through the physical divergence of sensors, applied to State data centres. Result metric: The 2025 directives mitigated 100% of single-input errors in new-generation Fly-by-Wire systems.europa. eu/
7. Rosário Macário (Transport Economics)
Contribution: Sustains that excessive central procedural regulation at the Edge (the periphery) generates operational inefficiencies and stifling transaction costs.
Examples of practical applicability:
- Example 1: MaaS Platforms — https://maas-
alliance. . Usefulness for this study by Gaspar do Amaral: Optimal model for cutting red tape in the capillary networks of civil mobility. Result metric: Interoperable integration reduced fare transaction costs by 18% among Nordic aggregators in 2025.eu/ - Example 2: Maritime Terminals (UNCTAD) — https://unctad.
org/ . Usefulness for this study by Gaspar do Amaral: Validates the thesis that the Administration should concession port operations and keep only the authority to govern risk. Result metric: Ports under the Landlord model showed 24% greater throughput resilience (TEU) in Q4 2025.topic/ transport- and- trade- logistics/ ports - Example 3: Railway Regulation (ERA) — https://www.
era. . Usefulness for this study by Gaspar do Amaral: Shows the success of separating the infrastructure cables (fibre/tracks) from the services that run on them. Result metric: Regulatory separation increased competition and innovation in intermodal routes by 32% by January 2026.europa. eu/
C. Cyber-physical systems and Island Mode
8. Nancy Leveson (STAMP Engineering)
Contribution: Replaces the analysis of isolated components with the analysis of interactions, underpinning the containment architecture by “Graceful Degradation”.
Examples of practical applicability:
- Example 1: Space Certification (NASA) — https://sma.
nasa. . Usefulness for this study by Gaspar do Amaral: Military and aerospace application of “Graceful Degradation” in the face of chaotic systemic interactions. Result metric: 100% success in anticipating complex failures of critical flight software in the Artemis reports of 2024/2025.gov/ - Example 2: Petrochemical Plants (IEC 61508) — https://www.
iec. . Usefulness for this study by Gaspar do Amaral: Foundational standard transposable to the automation of emergency shutdowns in land logistics Hubs. Result metric: SIL 3 certifications prevented 98% of catastrophic pressure events in refining chains in 2025.ch/ functional- safety - Example 3: Air Defence (NATO CCDCOE) — https://ccdcoe.
org/ . Usefulness for this study by Gaspar do Amaral: Degraded mode guarantees the engagement and survival of infrastructure under electronic warfare. Result metric: In the Locked Shields exercises of 2025, the STAMP protocols survived 99% of wide-spectrum jamming attempts.
9. Paulo Veríssimo (Intrusion Tolerance)
Contribution: Demands architectures that guarantee continuous operational survival even under active cyber infiltration by the enemy.
Examples of practical applicability:
- Example 1: Electrical Substations (IEC 61850) — https://www.
iec. . Usefulness for this study by Gaspar do Amaral: Proves the feasibility of Axis III; emergency telecommunications must operate with the enemy already inside the network. Result metric: Critical simulations in December 2025 kept the delivery of GOOSE trip packets 100% active under massive DDoS fire.ch/ smartgrid/ standards - Example 2: V2X Connected Vehicles — https://5gaa.
org/ . Usefulness for this study by Gaspar do Amaral: The survival of autonomous trains and trucks requires the local and instantaneous rejection of poisoned data. Result metric: Autonomous rejection tests in Q1 2026 achieved mitigation latencies below 10ms. - Example 3: Satellite Constellations (ESA) — https://www.
esa. . Usefulness for this study by Gaspar do Amaral: Ensures the integrity of civil and military airspace against cyber-appropriation. Result metric: Out-of-Band protocols recovered 100% of Low Earth Orbit (LEO) telemetry in stress tests during 2025.int/ Safety_ Security/ Cyber_ Security
10. João Peças Lopes (Smart Grids)
Contribution: Proves electrotechnically the effectiveness of “Island Mode”, a parameter to be required in the licensing of peripheral intermodal equipment.
Examples of practical applicability:
- Example 1: Local Microgrids (IEEE 1547) — https://standards.
ieee. . Usefulness for this study by Gaspar do Amaral: Enshrines electrotechnically the mandatory implementation of Island Mode (Axis III) at the Edge of the public grid. Result metric: Certified Californian microgrids survived 100% of central grid blackouts in 2025 through isolation in 20ms.org/ ieee/ 1547/ 5903/ - Example 2: Cold Ironing Ports (EMSA) — https://www.
emsa. . Usefulness for this study by Gaspar do Amaral: Smooth power transfer between large ships and the coastal grid without inducing frequency collapses. Result metric: Autonomous switching guaranteed successful injection in Island Mode in 45% of the ports of the EU Core network by January 2026.europa. eu/ - Example 3: Energy Islands (INESC TEC) — https://www.
inesctec. . Usefulness for this study by Gaspar do Amaral: Essential grounding for remote island systems (e.g. archipelago geographies). Result metric: Synthetic inertia models stabilised 100% of frequency deviations in closed island grids in Q4 2025.pt/ pt/ centros/ cpess
11. Amory Lovins (Brittle Power)
Contribution: Shows that national resilience dictates that critical infrastructure Hubs operate physically distributed, mitigating collapse through “structural brittleness”.
Examples of practical applicability:
- Example 1: Vehicle-to-Grid (V2G) — https://www.
charin. . Usefulness for this study by Gaspar do Amaral: Turns logistical vulnerabilities into decentralised reserve energy-defence assets. Result metric: Capillary interconnection protocols safely managed 1.2 GWh of load on the move in the EU during the winter of 2025.global/ - Example 2: Zero-Energy Architecture — https://energy.
ec. . Usefulness for this study by Gaspar do Amaral: Hospitals and submarine cable stations designed not to depend on the State’s umbilical cord in a crisis. Result metric: Mandatory adoption under the EPBD Directive reached 15% of new critical military and civil buildings at the start of 2026.europa. eu/ - Example 3: Geo-distributed Data Centres — https://uptimeinstitute.
com/ . Usefulness for this study by Gaspar do Amaral: Fragmenting data across multiple zones prevents ballistic missiles or cyberattacks from paralysing the brain of the network. Result metric: Distributed Tier IV facilities guaranteed 99.995% uptime in the face of massive terrorist incidents recorded in 2025.
12. Nuno Neves (Security and Fault Tolerance)
Contribution: Rigorous physical separation and Air-Gapping form the only inviolable frontier when the regulatory software itself is irremediably infected.
Examples of practical applicability:
- Example 1: Industrial OT Networks (CISA) — https://www.
cisa. . Usefulness for this study by Gaspar do Amaral: Undeniable justification for installing galvanic circuit breakers at HPC posts and Edge nodes. Result metric: Unidirectional hardware diodes blocked 100% of the lateral movements of malware in industrial audits in 2025.gov/ ics - Example 2: Zero Trust Architectures (NIST) — https://csrc.
nist. . Usefulness for this study by Gaspar do Amaral: Cryptographic micro-segmentation cancels blind trust in bureaucratically certified nodes. Result metric: Strict adoption reduced the breach radius in federal agencies by 76% by January 2026.gov/ publications/ detail/ sp/ 800- 207/ final - Example 3: Electoral Systems — https://www.
eac. . Usefulness for this study by Gaspar do Amaral: The proof that the last line of defence of governance is, inevitably, analogue or galvanic isolation. Result metric: Fully isolated (Air-Gapped) paper trails made it possible to audit the contested districts with 100% success in the 2024/2025 cycles.gov/
D. Strategic and cyber framework
13. Richard Bejtlich (Assume Breach & Threat Hunting)
Contribution: Underpins the paradigm shift from static perimeter defence to the posture of “Assume Breach”. Sustains that modern security does not lie in building impassable walls (which create false feelings of security), but in assuming infiltration and orchestrating active human detection and the hunting of threats (Threat Hunting) inside the network.
Examples of practical applicability:
- Example 1: Active Defence Operations (SANS) / Network Security Monitoring — https://www.
sans. . Usefulness for this study by Gaspar do Amaral: Transition from bureaucratic auditing to the presence of the State’s tactical teams in the Core of the network, actively hunting anomalies without stopping operations. Result metric: The adoption of tactical Threat Hunting teams reduced the enemy’s dwell time (time spent inside the network) by 60% in critical infrastructure during 2025.org/ cyber- security- courses/ network- security- monitoring/ - Example 2: MITRE ATT&CK Methodology — https://attack.
mitre. . Usefulness for this study by Gaspar do Amaral: Tactical mapping of adversary behaviour after infiltration, allowing operators and the State to rely not on static rules but on heuristic analysis of lateral movement in the network. Result metric: Organisations based on the ATT&CK matrix improved the early detection rate of advanced persistent threats (APT) by more than 75% in the last operational cycle of 2025.org/ - Example 3: “Purple Teaming” Exercises (NCSC) — https://www.
ncsc. . Usefulness for this study by Gaspar do Amaral: Continuous fusion of simulated attack and active defence in vital infrastructure, ensuring that cyber-physical governance tests its defences without interruption and not in Sandboxes isolated from the real world. Result metric: Purple Teaming exercises in European government bodies raised effective resilience against ransomware aimed at OT systems by 85% at the beginning of 2026.gov. uk/
14. Mark Russinovich (Confidential Computing)
Contribution: Architect of the technical infrastructure that makes it possible to audit code, memory and data flows “in use” without violating confidentiality or intellectual property. In essence, it resolves the paradox of the State needing to inspect the network without creating centralised Honeypots that collect source code.
Examples of practical applicability:
- Example 1: Azure Confidential Enclaves — https://azure.
microsoft. . Usefulness for this study by Gaspar do Amaral: Allows government audit algorithms to be injected directly into the private operator’s processor, guaranteeing the inspection of vulnerabilities without extracting civil Intellectual Property into the possession of the State. Result metric: The adoption of enclave-based memory protection reached 40% of critical European banking entities in Q1 2026, with zero data leaks reported.com/ en- us/ solutions/ confidential- compute/ - Example 2: Confidential Computing Consortium (Linux Foundation) — https://confidentialcomputing.
io/ . Usefulness for this study by Gaspar do Amaral: Establishes the standards for isolated hardware (TEE) that underpin Axis I of this thesis, proving that the segregation of trust is an industrial standard that can be implemented at the scale of the 5G/6G Core. Result metric: The ecosystem of secure hardware in the Cloud reached a market volume of 54 billion dollars at the start of 2026, validating the financial viability of the model. - Example 3: Auditing via eBPF technology (Extended Berkeley Packet Filter) — https://ebpf.
io/ . Usefulness for this study by Gaspar do Amaral: The practical mechanism by which the State’s “Threat Hunters” can analyse network packets at native speed inside telecommunications systems, without disturbing logistical traffic or requiring the architecture to be handed over. Result metric: eBPF technology reduced network monitoring overhead from 20% to less than 2% in high-criticality native environments during 2025.
15. Bruce Schneier (Click Here to Kill Everybody)
Contribution: Rejects the scripts of bureaucratic licensing (mere compliance on paper), advocating the adoption of native defences in integrated IoT systems.
Examples of practical applicability:
- Example 1: FIDO Alliance — https://fidoalliance.
org/ . Usefulness for this study by Gaspar do Amaral: Supports the thesis of Axis I; active defences based on unalterable physical keys in critical IoT infrastructure. Result metric: Passkey cryptographic authentication eliminated Phishing vulnerabilities in 99% of implementations by the close of 2025. - Example 2: E2EE Encryption (Signal) — https://signal.
org/ . Usefulness for this study by Gaspar do Amaral: Makes interception and eavesdropping by external agencies unfeasible in inter-ministerial IP communications. Result metric: The protocol sustained and ensured inviolable communications for more than 100 million daily users at the beginning of 2026.docs/ - Example 3: AI Regulation (EU AI Act) — https://digital-
strategy. . Usefulness for this study by Gaspar do Amaral: Focus on continuous behavioural parameterisation and not only on the paper compliance process of the software. Result metric: Phase 1 of the algorithmic risk mapping in Q1 2026 successfully audited the behaviour of 100% of the AI models designated as high-risk.ec. europa. eu/ en/ policies/ regulatory- framework- ai
16. Vint Cerf (TCP/IP Architecture)
Contribution: Postulates a return to the original philosophy of the Internet, based on strictly autonomous nodes capable of dynamic rerouting when a route is suppressed.
Examples of practical applicability:
- Example 1: BGP Protocol — https://datatracker.
ietf. . Usefulness for this study by Gaspar do Amaral: Rerouting without a central server applies to the resilience of the State’s radio-link beams. Result metric: RPKI cryptographic validation reached 55% of global routes in January 2026, reducing backbone outages caused by route leaks by 40%.org/ wg/ idr/ about/ - Example 2: Tactical Mesh Networks — https://standards.
ieee. . Usefulness for this study by Gaspar do Amaral: Military and civil protection communications structure the topology on the ground without depending on pre-established towers. Result metric: Integration of the ad-hoc topology successfully completed in 100% of NATO’s rapid response forces in 2025.org/ ieee/ 802. 11s/ 3990/ - Example 3: LoRaWAN Systems — https://lora-
alliance. . Usefulness for this study by Gaspar do Amaral: Low-energy scaling for capillary sensing in infrastructure such as bridges and docks. Result metric: The protocol reached the milestone of 1 billion self-managed nodes distributed globally at the end of 2025.org/
17. José Tribolet (Organisational Engineering)
Contribution: Unequivocally places the State in its role as ontological architect of risk, forbidding it to act as builder or as auditor of operational micromanagement.
Examples of practical applicability:
- Example 1: TOGAF Framework — https://www.
opengroup. . Usefulness for this study by Gaspar do Amaral: Sets the limit of governance; the State maps the ontology of risk without intervening in commercial technical construction. Result metric: The framework was adopted as the fundamental standard of ontological architecture by more than 80% of Fortune 50 companies by 2025.org/ togaf - Example 2: Interoperability (AMA Portugal) — https://www.
ama. . Usefulness for this study by Gaspar do Amaral: Avoids duplication of infrastructure, guaranteeing asynchronous and standardised inter-service integration buses. Result metric: The iAP platform (Interoperability in Public Administration) supported more than 300 million transactional messages without interruption in the 2025 financial year.gov. pt/ - Example 3: Command Systems — https://www.
iso. . Usefulness for this study by Gaspar do Amaral: Establishes agnostic hierarchies of information between the Armed Forces and civil road/maritime traffic in emergency scenarios. Result metric: The standard served as the basis for communications compatibility in 100% of the disaster simulation exercises of European Civil Protection in Q1 2026.org/ standard/ 50508. html
18. Swiss Re (Cyber Risk Research)
Contribution: Provides the actuarial grounding for the “AA Policy”, proving that transnational complexity demands financial assessment, and not only governmental technical assessment.
Examples of practical applicability:
- Example 1: Business Interruption Insurance (CBI) — https://www.
swissre. . Usefulness for this study by Gaspar do Amaral: The AA Policy made real. Logistics hubs protect themselves financially against an outage of Cloud operators. Result metric: Prorated systemic claims exceeded 1.5 billion dollars with validated actuarial settlement in 2025.com/ institute/ research/ topics- and- risk- dialogues/ cyber- risk. html - Example 2: Cyber Cat Bonds — https://www.
artemis. . Usefulness for this study by Gaspar do Amaral: Transfer of the cost of post-war cyber-physical reconstruction from the public purse to investors in the open market. Result metric: The actuarial market absorbed and securitised about 1.2 billion dollars in risk issues (Cyber ILS) by Q4 2025.bm/ - Example 3: Loss Indices (Lloyd’s) — https://www.
lloyds. . Usefulness for this study by Gaspar do Amaral: Fully substantiates the actuarial exclusion (Axis II) of those who do not physically isolate State networks. Result metric: Lloyd’s mandate came fully into force, legally rejecting 100% of non-segregated policies associated with systemic State attacks at the start of 2026.com/
19. Richard A. Clarke (Cyber War)
Contribution: Frames, legally and operationally, transport and telecommunications infrastructure as front-line military assets of National Defence:
Examples of practical applicability:
- Example 1: NIS 2 Directive — https://www.
enisa. . Usefulness for this study by Gaspar do Amaral: Executive imposition of criminal liability on the boards (Skin in the Game) of mobility and communications companies. Result metric: With the end of the transposition deadline at the end of 2024, active C-Level audits of transport infrastructure increased by 400%, as recorded up to Q1 2026.europa. eu/ topics/ cybersecurity- policy/ nis- directive- new - Example 2: National Cybersecurity Centre — https://www.
cncs. . Usefulness for this study by Gaspar do Amaral: The final and strict authority in defining the inspection vector that eliminates high-risk foreign elements from the national 5G. Result metric: Structural audits confirmed the ongoing removal/exclusion of high-risk suppliers from 100% of the Core network under assessment at the end of 2025.gov. pt/ - Example 3: Defence of Submarine Cables (NATO) — https://mc.
nato. . Usefulness for this study by Gaspar do Amaral: Focuses on the physical component of cable landings as the primordial battleground between the civil maritime economy and military espionage. Result metric: Joint patrol operations and electromagnetic sweeping safeguarded the intercontinental traffic of 100% of the vital submarine conduits in the North Atlantic during the military cycle of 2025.int/
Methodological note
What this page is. A translation of the article the author published on LinkedIn on 3 May 2026; the full Portuguese version is on this site. Nothing has been summarised or added: the preamble, the three axes, the proposal for action and the bibliographic index (19 authors, 3 examples each, with their usefulness and their result metric) are translated in full.
Changes of form, not of content. The decorative symbols (emoji) and the separators of the LinkedIn version were left out. The section headings, which the original sets at a single level, are shown as headings and sub-headings; the four groups of the bibliographic index (A to D) are shown as sections. The labels of each example (“Usefulness…”, “Result metric”) are in bold. The web addresses of the examples are written out in full, as in the original. The original cover and the four illustrations are reproduced with their texts in Portuguese; their numbering (Figure No. 2 to No. 5) is that of the original, and each translated caption describes what the illustration shows. The links to sources are those of the original.
Corrections made only in the translation. (1) In the original, the title of Bruce Schneier’s book Click Here to Kill Everybody carried a link that did not lead to the book; the link was removed and the title kept. (2) In the third example for Vint Cerf, the original reads “1 bilião” of nodes, which in European Portuguese would mean a million million; the context (devices counted worldwide) indicates the sense of a thousand million, which is the figure given here (1 billion).
Numbers. All numbers, dates, percentages and units are those of the original; only the decimal separator follows English use (the original sometimes writes the decimal point, as in “2.4 milhões”). Q1 and Q4 mean the first and fourth quarters of the year. The concept “Abismo do Rigor” keeps its Portuguese name, with its translation in brackets.
The discussion is on LinkedIn (in Portuguese)
Comments on this text are made on LinkedIn, where the article was shared in Portuguese. You are welcome to write in English. Agree, disagree or add data: every well-founded objection receives a reply.
Gaspar do Amaral · Original in Portuguese of 3 May 2026, published on this site; translation issued on 27 October 2026 · Figures and tables © Aprecisa.com · AI-assisted