 ← Grupo Aprecisa · Connecting those who know with those who need
Cybersecurity and digital sovereignty · Proposals submitted to the public consultation of 14 April 2026
From Regulatory Compliance to Operational Resilience: 10 Proposals for the New Cybersecurity Framework
Ten proposals so that Portugal’s new cybersecurity framework (NIS 2) moves from compliance on paper to real resilience
Gaspar do Amaral · 14 April 2026
Translated from the Portuguese original. This version was issued on 27 October 2026.
On this site, this article has been
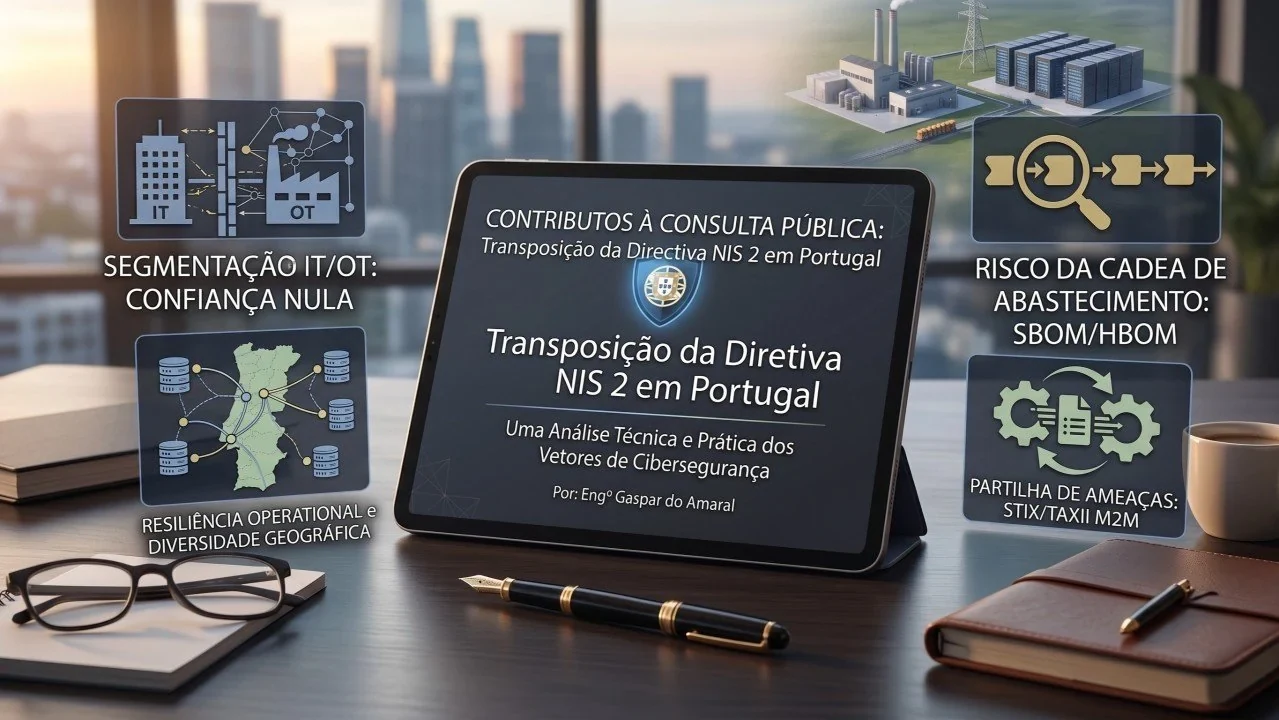
The cybersecurity paradigm has changed. And regulation must keep pace with engineering.
Over more than three decades designing and integrating complex land, maritime and air communications systems, I have learnt one undeniable lesson: paper accepts anything, but the physics of networks does not forgive.
Portugal is currently discussing the new Regulamento do Regime Jurídico de Cibersegurança (the regulation of Portugal’s legal framework for cybersecurity), which transposes the NIS 2 Directive. It is a formidable regulatory milestone. However, if we look at the global landscape of critical infrastructure, technical and scientific rigour demands that we move from mere administrative compliance to true cyber-physical resilience.
I have summarised 10 proposals that I have already submitted to the public consultation. They are also supported by the views of the world’s leading experts and are already applied in the most mature regions of the globe:
1. The end of blind trust: tactical IT/OT isolation
We cannot treat the networks that run ports or airports (OT, operational technology) in the same way as the office Wi-Fi (IT, information technology).
- The authors’ view: John Kindervag (USA), the architect of the Zero Trust model, showed that trust is a vulnerability. Joe Weiss and Robert M. Lee have warned for years that IT/OT convergence without micro-segmentation is lethal for physical operations.
- Global application: Following the attack on Colonial Pipeline, the TSA in the USA actively imposed Zero Trust on industrial systems, requiring that the corporate attack surface never serves as a bridge to the factory floor.
As it stands (systemic vulnerability): There is currently a “false redundancy”, and IT and OT networks are often treated as converged, which allows ordinary cyberattacks on the corporate network to paralyse critical operations.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): With the proposed addition, the regulation will impose “tactical isolation” through mandatory micro-segmentation between the IT and OT domains for all Essential Entities (IEC 62443 standard).
2. An X-ray of the supply chain (SBOM/HBOM)
The risk we inherit from our suppliers is our biggest blind spot.
- The authors’ view: Allan Friedman (the “father” of SBOM at CISA) argues that we cannot protect what we do not know we have. Bruce Schneier reminds us that complexity is the enemy, while Ciaran Martin showed how dependence on unscrutinised Tier 1 suppliers compromises national sovereignty.
- Global application: The United Kingdom led the blocking of high-risk suppliers (Telecommunications (Security) Act 2021), while the USA, through Executive Order 14028, made the SBOM mandatory for government suppliers.
As it stands (systemic vulnerability): The current state is one of “inherited risk”: critical entities do not have full visibility of the technical make-up (hardware and software) they use.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): The suggested amendment will require the mandatory delivery of the Software Bill of Materials (SBOM) and the Hardware Bill of Materials (HBOM) for critical equipment, mitigating inherited risk at the root of the infrastructure.
3. The illusion of redundancy and the need for diversity
Running two fibre-optic cables along the same trench is not redundancy; it is a single point of failure waiting for an excavator.
- The authors’ view: Richard Danzig argues for “surviving failure”, building systems that tolerate collapse. Mikko Hypponen coined “Hypponen’s Law”: if it is “smart”, it is vulnerable. Kim Zetter illustrated this in her work on Stuxnet.
- Global application: In Singapore, the MAS TRM guidelines now require absolute geographic and logical diversity, mandating Out-of-Band management channels (OOBM) that are 100% segregated from the internet.
As it stands (systemic vulnerability): The current requirement for mere “redundancy mechanisms” allows systems to share the same physical paths (common trenches), creating a single point of failure.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): It will be mandatory to implement fully segregated Out-of-Band Management (OOBM) networks, guaranteeing the ability to carry out recovery manoeuvres if the main network is totally disrupted.
4. Systemic threats demand responses at machine speed (M2M)
Reporting incidents through manual forms means acting when the neighbouring infrastructure has already been compromised.
- The authors’ view: David Koh (Singapore) is the evangelist of automated cyber intelligence. Eugene Kaspersky warns that industrial malware spreads at speeds that human bureaucracy cannot stop.
- Global application: ENISA and CISA operate Automated Indicator Sharing platforms using the STIX and TAXII protocols.
As it stands (systemic vulnerability): Reporting is currently manual, which introduces a fatal delay in the face of industrial malware.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): The regulation will require the adoption of M2M protocols (STIX/TAXII) so that the “logical vaccine” is distributed instantly across the whole national network.
5. The end of “generic MFA”: phishing-resistant authentication
- The authors’ view: Andrew Shikiar (FIDO Alliance) promotes unbreakable cryptographic credentials. CISA issued memoranda to ban authentication by SMS in federal agencies.
As it stands (systemic vulnerability): Annex III (PR.GA-3) only requires generic “MFA” (multi-factor authentication), which is vulnerable to interception attacks (AiTM, adversary-in-the-middle).
As it will be (proposal by Gaspar do Amaral, 14 April 2026): An explicit requirement for phishing-resistant MFA (FIDO2/PKI) for administration profiles in critical infrastructure.
6. The post-quantum leap (PQC) and the integrity of AI
- The authors’ view: Peter Shor showed how quantum computers will break RSA encryption. NIST has already published the final standards for PQC algorithms.
As it stands (systemic vulnerability): The installed infrastructure is blind to the algorithms that will become obsolete with quantum computing.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): A requirement for a “Cryptographic Inventory” (ID.GA-2) and integrity controls against data poisoning attacks on AI.
7. Cyber insurance as a risk-transfer tool
- The authors’ view: The World Economic Forum advocates cyber insurance as the last bastion of financial resilience.
As it stands (systemic vulnerability): There are no mechanisms for immediate liquidity in large-scale disaster recovery processes.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): Cyber insurance included as an assessment measure for risk transfer (GR.GR-3), forcing alignment with audited standards of rigour.
8. From static testing to continuous red teaming and bug bounties
- The authors’ view: Katie Moussouris demonstrates the effectiveness of collective intelligence. The TIBER-EU framework is the European standard for tests by real attackers.
As it stands (systemic vulnerability): Announced penetration tests of limited scope create a false sense of security.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): Annual red teaming exercises and bug bounty programmes to detect flaws proactively.
9. Human engineering and capability gap analysis
- The authors’ view: The SANS Institute shows that investment in awareness fails without a mapping of skills (the skills gap).
As it stands (systemic vulnerability): Policies based on generic awareness curricula that do not keep pace with the complexity of the threats to the productive fabric.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): An Annual Capability Gap Analysis made institutional, based on the NICE Framework (NIST), investing surgically where there is a shortfall in defence engineering.
10. Integrity in algorithms and artificial intelligence
- The authors’ view: International standardisation bodies expect AI to become the cornerstone supporting the operation of critical infrastructure in the coming years.
As it stands (systemic vulnerability): Deliberate data poisoning in untraceable systems can lead to anomalous behaviour of cyber-physical systems and to infrastructure shutdowns.
As it will be (proposal by Gaspar do Amaral, 14 April 2026): Mandatory detailed documentation of the chain of custody and provenance of training data in Artificial Intelligence and Machine Learning systems that support critical operations, ensuring auditability and preventing manipulation.
Conclusion: from paper to cyber-physical sovereignty
Final resilience is not decreed on a sheet of paper; it is built with rigour and engineering on the ground. These 10 proposals are contributions to the foundations on which our digital sovereignty must be raised.
The debate is open. I count on your contribution and your technical rigour in the comments.
Gaspar do Amaral (the proposals were submitted to the public consultation on 14 April 2026)
Bibliography
1. Map of authors and engineering concepts
- Kindervag, John: principal architect of the Zero Trust architecture. Reference: NIST SP 800-207 (Zero Trust Architecture).
- Weiss, Joe: industrial control systems (ICS) engineer focused on the cyber-physical security of OT. Reference: ISA/IEC 62443, the standard for industrial automation and control systems.
- Lee, Robert M.: founder of Dragos (ICS security) and creator of a tactical industrial security methodology. Reference: The Dragos ICS Cybersecurity Maturity Model.
- Friedman, Allan: software architect at CISA, focused on supply-chain transparency. Reference: CISA Software Bill of Materials (SBOM) Framework.
- Schneier, Bruce: technologist and security analyst, focused on complexity as a systemic vulnerability. Reference: Complexity as the Worst Enemy of Security.
- Martin, Ciaran: founder and former head of the United Kingdom’s National Cyber Security Centre (NCSC), focused on national security and Tier 1 dependencies. Reference: NCSC Active Cyber Defence Programme.
- Danzig, Richard: senior fellow of the Center for a New American Security (CNAS), focused on “surviving failure” architectures. Reference: The Technology Risk Management Framework for Surviving Disruption (CNAS Paper).
- Hypponen, Mikko: research architect at WithSecure (Finland) and coiner of “Hypponen’s Law”. Reference: Law of IoT Vulnerability (F-Secure Technical Keynote).
- Zetter, Kim: investigative journalist and specialist in advanced industrial malware. Reference: Countdown to Zero Day: Stuxnet and the Launch of the World’s First Digital Weapon (investigative work); related information from CISA.
- Koh, David: Commissioner of Singapore’s Cyber Security Agency (CSA), leading evangelist of automated cross-border cyber intelligence. Reference: Singapore MAS TRM Guidelines (section on M2M automation).
- Kaspersky, Eugene: CEO and founder of Kaspersky Lab, focused on the spread of advanced industrial malware. Reference: The Velocity of Industrial Malware Propagation (Kaspersky Report).
2. Map of directives and global examples
- TSA in the USA (Colonial Pipeline attack): binding tactical directive for the energy and transport sector. Reference: TSA Security Directive Pipeline-2021-02 (Zero Trust Industrial Implementation).
- United Kingdom (blocking of suppliers): telecommunications security law for the scrutiny of Tier 1 suppliers. Reference: Telecommunications (Security) Act 2021 (UK) – High-Risk Vendor Removal.
- USA, Executive Order 14028: federal executive order on improving the nation’s cybersecurity. Reference: Executive Order 14028 (Improving the Nation’s Cybersecurity) – SBOM section.
- Singapore, MAS (Asia-Pacific): technology risk management guidelines for critical financial and transport infrastructure. Reference: MAS Technology Risk Management (TRM) Guidelines – geographic diversity and Out-of-Band Management (OOBM).
- ENISA in Europe (STIX/TAXII): platforms for cooperation and intelligence sharing at machine speed. Reference: ENISA Technical Guideline on Automatic Information Sharing – M2M protocol STIX/TAXII.
- CISA in the USA (STIX/TAXII): automated system for sharing indicators of compromise (IoC). Reference: CISA Automated Indicator Sharing (AIS) – M2M protocol STIX/TAXII.
Methodological note
What this page is. A translation of the article the author published on LinkedIn on 14 April 2026; the full Portuguese version is on this site. The ten proposals were submitted on the same day to the public consultation run by the CNCS (Centro Nacional de Cibersegurança, Portugal’s National Cybersecurity Centre).
Names of laws. The Directive is cited by its official English name, Directive (EU) 2022/2555 (NIS 2 Directive). Portuguese instruments with no official English translation, such as the Regulamento do Regime Jurídico de Cibersegurança, are kept in Portuguese with an explanation in brackets. The British law is cited by its official name, Telecommunications (Security) Act 2021.
Changes of form, not of content. The decorative symbols (emoji) of the LinkedIn version were left out. The codes PR.GA-3, ID.GA-2 and GR.GR-3 (controls in Annex III of the draft regulation), which LinkedIn had turned into false web links, appear as plain text. The original illustration is reproduced with its texts in Portuguese and a translated caption. The links to sources are those of the original.
What happened next. In June 2026 the CNCS classified all ten proposals as “Não acolhido” (not accepted). The author’s assessment of that verdict is in the article “The New Cybersecurity Framework: What Was Left Undone”.
The discussion is on LinkedIn (in Portuguese)
Comments on this text are made on LinkedIn, where the article was shared in Portuguese. You are welcome to write in English. Agree, disagree or add data: every well-founded objection receives a reply.
Gaspar do Amaral · Original in Portuguese of 14 April 2026, published on this site; translation issued on 27 October 2026 · Figures and tables © Aprecisa.com · AI-assisted